GovOps:
measure risk, transparency, and accountability
With declarative policies, formal analysis, explicit federation, and continuous compliance, organizations can finally govern in real time — matching the velocity of the systems they are securing.
Open Standards Solutions:


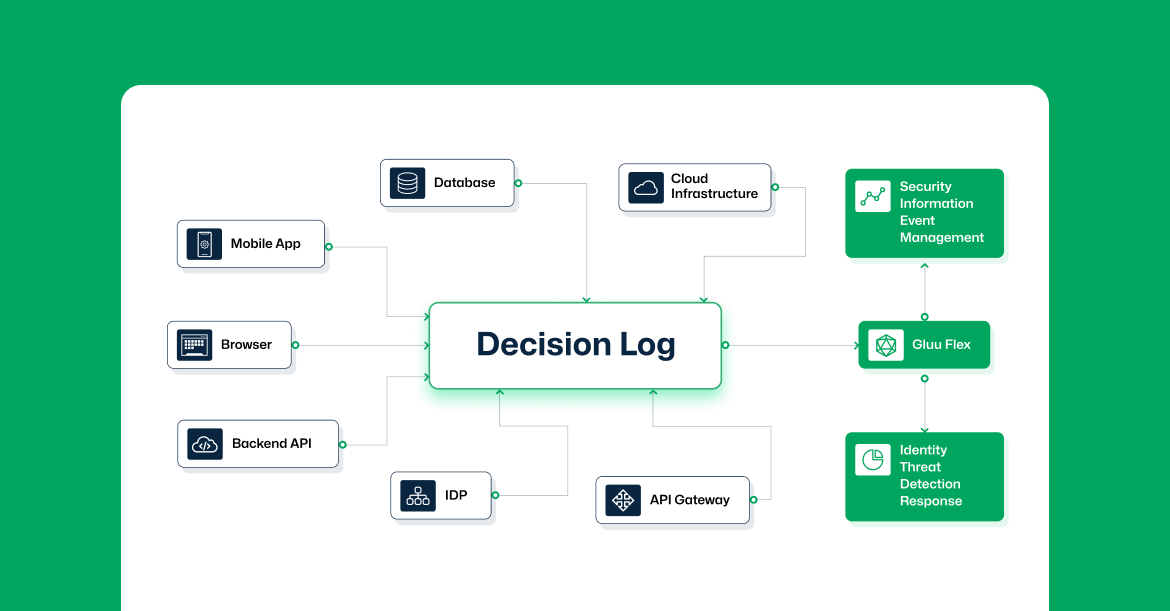
Real time decision logs provide the data your enterprise needs for threat detection and alerting.
Collect Logs
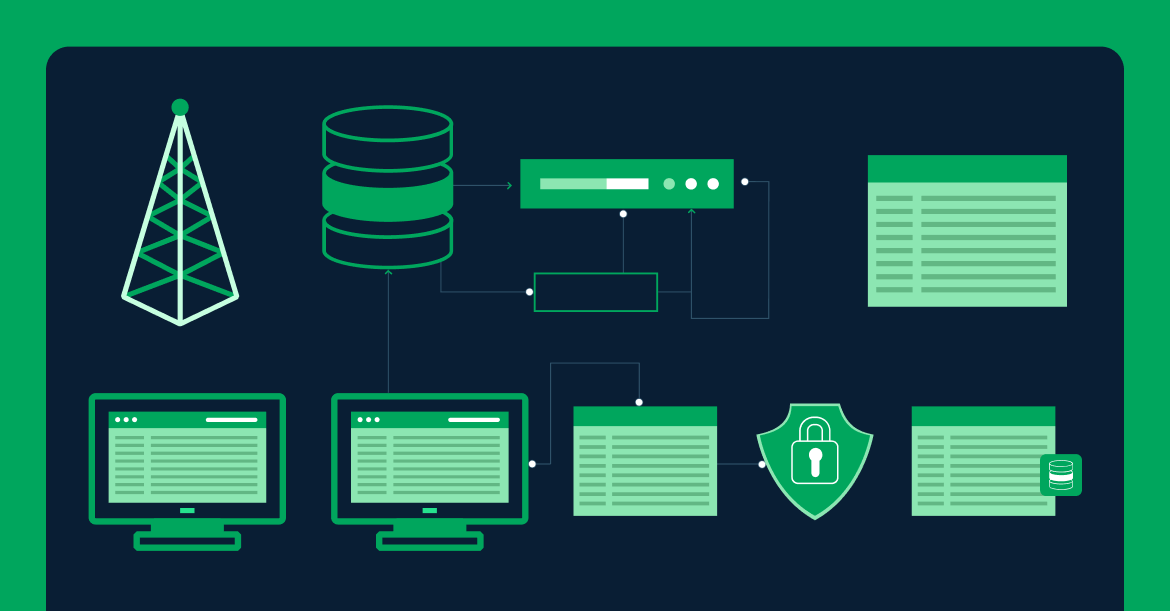
Gluu Flex collects all Cedarling decision logs, detailing everything that was both allowed and denied from the edge to the database.
Connect Logs
Gluu Flex connects authorization decision events to Identity Threat Detection and Response (“ITDR”) services for real time protection and fraud detection.
How does it work?
Author Policies
Enrich Tokens
Embed PDP
Respond To Threats
Components
Cedarling
An open source embeddable PDP that runs anywhere, returning authorization decisions based on declarative access policies.
Gluu Flex
Enterprise infrastructure that connects Cedarlings, provides OAuth-based workload and person identity, mints JWT tokens and publishes keys.
Agama Lab
Developer portal to author Cedar schema and policies, define low-code web and native authentication workflows, and manage Gluu Solo hosted infrastructure.
Janssen Project
Upstream open source project at the Linux Foundation which drives long term innovation of the core infrastructure.
JWT Validation
Validate Signatures
The Cedarling validates signatures against keys published by the issuer, and enforces the algorithm strength the enterprise requires.
Validate Contents
Depending on the type of token, certain claims must be checked — like “exp”, the expiration of the JWT.
Check Status
Confirm a JWT has not been revoked by fetching the issuer's latest OAuth Status List.
The Cedarlings log all decisions — allowed or denied. This rich source of information includes the tokens, policies, people, workloads, actions, resources, and context.
Gluu Flex streams data to SIEM and ITDR platforms for analysis and alerting. Gluu can call APIs for ITDR and SIEM SaaS vendors, providing the minimum required information to protect privacy and save costs.
Flex can authenticate people and software, using customizable front channel or back channel flows. It can even do this post-authentication to gather consent or step-up authentication to satisfy enterprise policies to protect certain resources.
Flex provides real time telemetry information about the currently active Cedarling instances at the edge of the network.
Cedarling instrumentation
Legacy Application Integration
Cedarling provides a risk-free way to enhance security insights for legacy applications. By instrumenting applications, Cedarling evaluates requests and logs decisions — without altering security behaviour.
Built for performance and flexibility, the Cedarling leverages Rust for fast execution, ensuring minimal impact on application performance. Security modernization doesn't have to be disruptive.
Cedarling performance
50 microsecond decisions
Speed matters in enterprise security. The Cedarling delivers authorization decisions in under 50 microseconds, ensuring zero performance bottlenecks. In the browser, mobile app, API gateway or database, the Cedarling's Rust-powered engine guarantees lightning-fast access control.
For enterprises where one millisecond means lost revenue, the Cedarling is the next-generation solution for secure, high-speed authorization.
Under
50µs
Privacy-first access control
Application Scoped JWTs
Mint a token per application, carrying only the claims that application needs, so no single token becomes a key to everything.
Application Scoped Policies
Policies are written and versioned per application in Git, which keeps the blast radius of a change to the application it belongs to.
Consent Workflows
Consent is captured as part of the authorization flow, and the record of it travels with the decision log.
OAuth Transaction Token Support
Transaction tokens carry business-specific context for a single operation, so downstream services can authorize without over-sharing identity data.
Still have a question?
Schedule a call with our pre-sales engineers to flush out if Gluu Flex makes sense for your business.